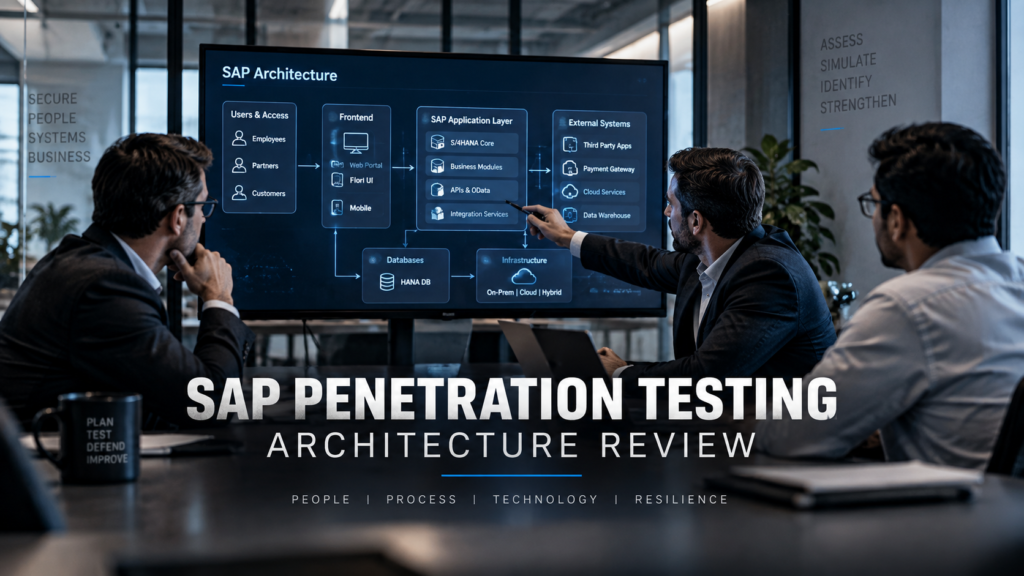
SAP penetration testing is the practice of simulating real-world attacks against an organization’s SAP ERP environment to identify exploitable vulnerabilities in configuration, custom code, authorization structures, and network exposure before an actual attacker finds them. It’s fundamentally different from standard web or network penetration testing, because SAP systems run the financial, HR, supply chain, and operational backbone of an enterprise – a compromised SAP environment doesn’t just expose data, it can halt business operations entirely. At BFRT, we’ve found that most enterprises approach SAP penetration testing with assumptions carried over from standard IT security testing, and those assumptions consistently leave critical gaps unaddressed.
Why SAP Systems Are a Different Kind of Target
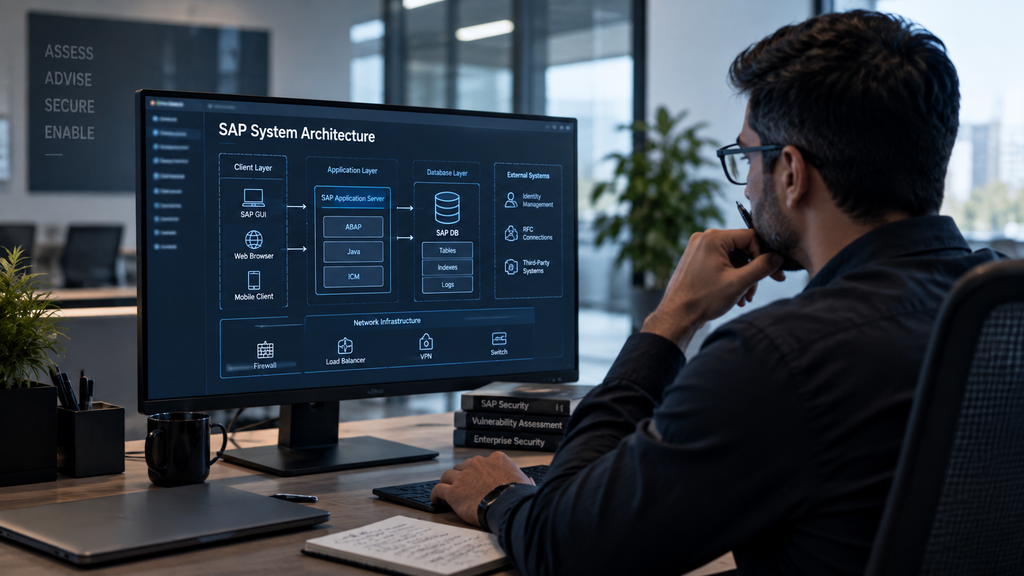
Unlike a typical web application, an SAP environment is a deeply interconnected system of modules, custom code, role-based authorizations, and integration points with other enterprise systems – finance, procurement, HR, and often external banking or logistics partners. This complexity means SAP penetration testing requires specialized knowledge of SAP-specific attack vectors, like RFC (Remote Function Call) exploitation, SAP GUI vulnerabilities, and misconfigured transport layers, none of which a generalist web application tester would typically know to check.
If you’ve read our breakdown of blended physical and digital red team engagements, you already understand our position on testing systems the way real adversaries actually approach them – SAP is no exception, and attackers who target ERP systems specifically look for these interconnections rather than isolated application flaws.
Mistake 1: Treating SAP Like a Standard Web Application
The most common mistake we see is organizations commissioning a generic web application penetration test and assuming it covers their SAP environment adequately. Standard web app testing methodologies – even thorough ones – don’t account for SAP-specific protocols like RFC, SAP GUI, or the Internet Communication Manager (ICM), which have entirely different vulnerability classes than standard HTTP-based applications.
SAP penetration testing requires testers who understand these protocols specifically, not testers applying OWASP Top 10 methodology to a system that operates fundamentally differently underneath.
Mistake 2: Only Testing the Application Layer, Not the Configuration
SAP systems ship with thousands of configuration parameters, and a significant portion of real-world SAP compromises stem from misconfiguration rather than application-layer vulnerabilities – default passwords on standard SAP users, overly permissive gateway configurations, or unsecured RFC destinations. A proper SAP penetration testing engagement audits these configuration layers explicitly, rather than only probing the application interface for input validation flaws.
We’ve found unsecured RFC connections during SAP penetration testing engagements that would have allowed lateral movement between production and development systems – a configuration gap invisible to anyone only testing the application surface.
Mistake 3: Ignoring Custom ABAP Code
Most enterprise SAP environments run substantial custom ABAP code layered on top of the standard SAP modules, and this custom code frequently introduces vulnerabilities that standard SAP security patches never address, because the vulnerabilities are unique to that organization’s specific customizations. SAP penetration testing that skips a code review of custom ABAP developments is missing one of the most common real-world attack surfaces in enterprise SAP deployments.
Mistake 4: Skipping Authorization and Segregation of Duties Testing
SAP’s authorization model is notoriously complex, and improperly configured roles can allow segregation of duties (SoD) conflicts – for instance, a single user having both purchase order creation and payment approval permissions, enabling fraud that has nothing to do with a traditional technical exploit. SAP penetration testing needs to include authorization and SoD analysis alongside technical vulnerability testing, since this is where some of the highest-impact business risk actually lives.
This is also where SAP penetration testing intersects directly with compliance frameworks like SOX and internal audit requirements, making it as much a governance exercise as a technical one.
Mistake 5: Testing in Isolation From the Broader Digital Transformation Review
Many enterprises commission SAP penetration testing as a standalone, one-time exercise disconnected from broader digital transformation initiatives – cloud migrations, S/4HANA upgrades, or integration with third-party platforms. Each of these changes introduces new attack surface that a prior SAP penetration testing engagement wouldn’t have covered, meaning the assessment goes stale faster than most organizations realize.
What a Proper SAP Penetration Testing Engagement Actually Covers
A comprehensive SAP penetration testing engagement should include network-level testing of SAP-specific ports and services, application-layer testing of SAP GUI and Fiori interfaces, configuration review of gateway and RFC settings, custom ABAP code review, and authorization/SoD analysis – each requiring distinct expertise that a single generalist tester rarely possesses across all five areas.
How BFRT Approaches SAP Penetration Testing
We treat SAP penetration testing as a specialized discipline requiring testers with direct SAP security experience, not general penetration testers extending their skill set into an unfamiliar system. Every engagement follows a defined rules of engagement process – similar to what we outlined in our physical red team rules of engagement guide – since testing a live production SAP environment carries real operational risk that needs explicit boundaries agreed upfront.
Understanding what SAP penetration testing actually requires – beyond a standard web application test – is the first step toward closing the gaps most enterprises don’t know exist in their ERP security posture. If your organization runs SAP and hasn’t had a specialized assessment covering configuration, custom code, and authorization structures, BFRT can walk you through what a proper engagement looks like for your environment.
Book a Call with BFRT’s SAP Team