Compromise Assessment vs Physical Red Team: 5 Key Differences
Compromise assessment vs physical red team is a comparison we get asked about constantly, and the short answer is this: a compromise assessment finds out
🔥 Trusted by banks and enterprises across 5 continents to find the gaps before attackers do. Grab $1,000 off your next engagement →
Understanding physical security terminology is essential for organizations responsible for protecting facilities, critical infrastructure, and sensitive data. As threats evolve, enterprises must evaluate not only cybersecurity defenses but also the resilience of their physical security controls.
This physical security glossary provides clear definitions of key terms used in physical penetration testing, red teaming, and enterprise facility security assessments. These concepts help organizations understand how attackers exploit physical vulnerabilities and how modern security programs mitigate those risks.
The glossary below covers common techniques, security controls, and testing methodologies used to evaluate the effectiveness of physical security programs.
Modern organizations face increasingly complex physical threats. Attackers may combine social engineering, credential misuse, insider assistance, and infrastructure weaknesses to gain unauthorized access to sensitive areas.
Understanding physical security terminology helps organizations:
Security leaders, facility managers, and risk professionals often rely on structured security terminology when planning security improvements and conducting risk assessments.
Below are key physical security terms commonly used in security assessments and red team engagements.

Compromise assessment vs physical red team is a comparison we get asked about constantly, and the short answer is this: a compromise assessment finds out
A physical red team report is the document that translates an intrusion test into decisions your organization can actually act on – and most CISOs
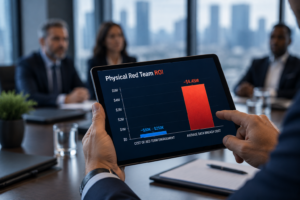
Physical red team ROI is the measurable value an organization gets from proactively testing its facilities against real intrusion tactics, weighed against the cost of
By Jaysinh Dabhi, Red Team Operations Head at Bluefire Redteam. 5+ years leading physical and digital red team operations across BFSI, data centre, and critical-infrastructure
By Jaysinh Dabhi, Red Team Operations Head at Bluefire Redteam. 5+ years leading physical and digital red team operations across BFSI, data centre, and critical-infrastructure
Introduction A multinational technology enterprise operating large corporate campuses in Pune and Gurugram engaged Bluefire Redteam to conduct a surprise physical penetration test across multiple
A real-world physical security assessment revealed how a widely used RFID-based access control system could be fully compromised using badge cloning techniques. In this case
A visitor management system (VMS) is a process or technology used to track, manage, and control visitor access within a facility. It ensures that all
An access control audit is a structured evaluation of an organization’s physical access control systems, policies, and procedures to ensure that only authorized individuals can
A physical security risk assessment is a structured process used to identify, evaluate, and prioritize risks related to unauthorized physical access, facility vulnerabilities, and security
Enterprises typically perform physical security testing when:
Periodic testing ensures that security policies, technology, and personnel procedures function as intended.
Understanding how attackers exploit physical vulnerabilities helps organizations implement stronger defenses.
| Attack Technique | Description | Typical Security Control |
|---|---|---|
| Tailgating | Unauthorized entry by following an authorized user | Mantrap systems, badge enforcement |
| Badge Cloning | Duplicating access credentials | Encrypted smart cards, MFA |
| Social Engineering | Manipulating employees to gain access | Security awareness training |
| Insider Privilege Abuse | Authorized users misusing access | Role-based access control |
| RFID Cloning | Wireless duplication of access credentials | Encrypted RFID credentials |
Organizations often identify these vulnerabilities during physical penetration testing assessments.
Understanding security concepts is important, but real-world testing shows how vulnerabilities are actually exploited.
Physical security testing is a critical component of modern enterprise security programs. Organizations seeking to validate the resilience of their facility defenses often engage specialized security teams to conduct controlled assessments.
To learn more about professional testing services, visit:
Understanding terminology is important, but organizations also need to plan budgets and engagement scope.
Learn more: Cost of Physical Penetration Testing
Penetration testing focuses on identifying vulnerabilities, while red teaming evaluates how well organizations detect and respond to simulated attacks.
Security professionals, facility managers, compliance teams, and executives responsible for risk management benefit from understanding physical security concepts.
What are you looking?
Trusted by customers in 7+ countries!